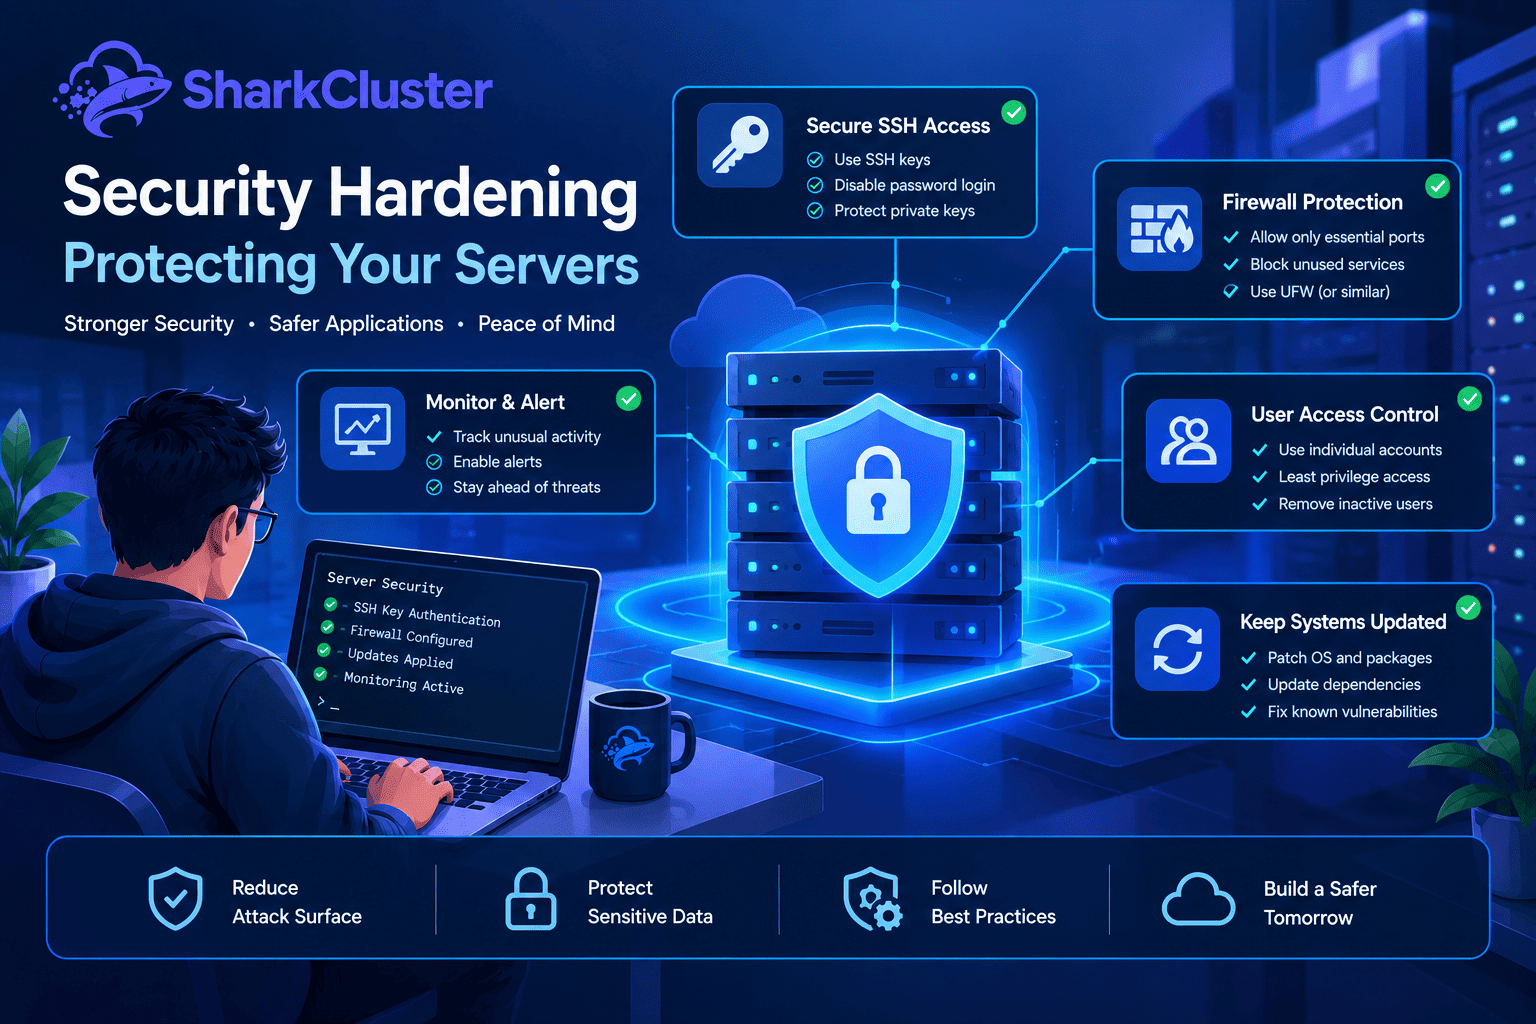
Server security remains essential throughout an application's lifecycle. After deployment, servers continue to face risks from unauthorized access, exposed ports, outdated software, and misconfigured services. Protecting your application requires more than a one-time setup: it means controlling server access, limiting network exposure, applying security updates, and monitoring potential threats.
Some common sources of server exposure are
- Weak or reused passwords
- Password-based SSH
- Unnecessary open ports
- Excessive user privileges
- Outdated operating system packages
- Unpatched application dependencies
- Missing SSL/TLS protection
- Lack of monitoring and alerting
- Services exposed on the public internet.
Hardening addresses these by following the principle of reducing the attack surface and limiting the impact of unauthorized access.
Additionally, layered security is required.A firewall alone is not sufficient, nor are SSH keys alone. Secure application configuration, access controls, encryption, monitoring, and regular updates should all work together.
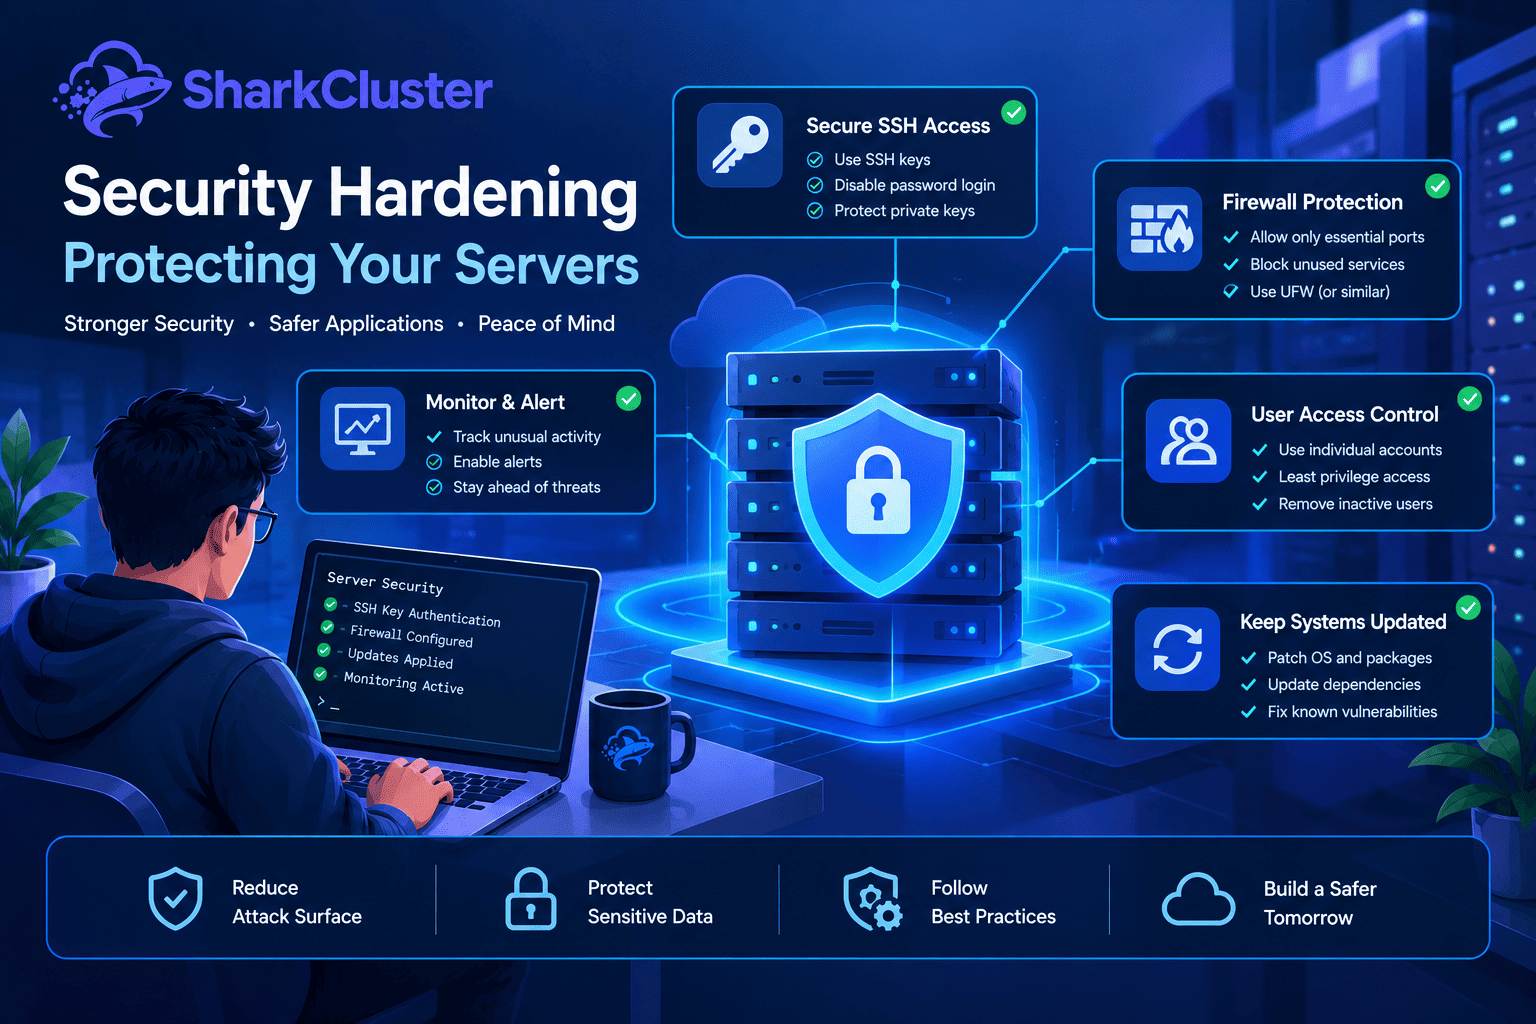
1. Securely manage SSH keys.
One of the most essential methods for management to gain access to a Linux server is SSH. Therefore, protecting it should be one of the first things you do to harden it.
Whenever possible, SSH key-based authentication should take the place of passwords. An SSH key pair consists of a public key that is installed on the server and a private key that is well-kept on the administrator's machine.
A basic key can be generated with:
ssh-keygen -t ed25519The authorized keys on the server can then be updated with the public key.
Administrators may consider disabling password authentication in the SSH configuration after attempting key-based access:
Disable Direct Root Login
For better SSH security, consider disabling direct root login and using a dedicated administrative account with the necessary privileges. Before changing the SSH configuration, verify that the alternative account can connect successfully and perform the required administrative tasks. Keep an existing session open until the new connection is confirmed.
PasswordAuthentication noAfter making changes to the SSH config, check it before reloading or restarting the service:
sudo sshd -tThen reload or restart SSH based on your operating system's service config.
Protect private keys
Never store your private SSH key in application directories, chat, or public repos. When necessary, make use of an SSH agent and a passphrase-protected key for additional security.
Also, review authorized keys periodically:
cat ~/.ssh/authorized_keysRemove keys not associated with an authorized administrator or deployment system.
Important: Be careful when changing SSH or firewall settings manually
Editing ~/.ssh/authorized_keys, SSH daemon settings, or firewall rules directly can interrupt your access to a server if the changes are incorrect. Depending on how SharkCluster applies and manages these settings, manual changes may also conflict with panel-managed configuration.
Before making changes, confirm the supported procedure in SharkCluster's documentation or with the development team. Keep your current SSH session open, verify that you have an alternative recovery method, and test a new connection before closing the existing session. Do not remove existing access keys or change SSH ports until the replacement access method has been verified.
2. Set up the firewall.
A firewall provides an additional crucial layer of protection by controlling which network connections can connect to the server.
You should block everything, but you should only allow ports that are essential to the operation of legitimate services.
For instance, a typical web server might need:
- SSH for administration
- HTTP for web traffic
- HTTPS for encrypted web traffic
Other services like databases shouldn't be publicly exposed unless it is a part of your architecture.
On Ubuntu systems using UFW, administrators can check their current configuration with:
sudo ufw status verboseA basic configuration might allow SSH, HTTP, and HTTPS:
sudo ufw allow OpenSSH
sudo ufw allow 80/tcp
sudo ufw allow 443/tcp
Then enable the firewall:
sudo ufw enableBefore applying a firewall change, make sure your current admin access will still be available
Accidentally blocking SSH can disconnect you from the server.
Additionally, whenever an application's architecture changes, firewall rules should be reviewed. If a service is removed, the public access to it should be removed as well.
3. Control User Access and Privileges
Not every administrator or application needs unrestricted access to a server.
Instead of sharing a single admin account, use individual user accounts to make access easier to audit and allow permissions to be revoked for a specific person and not everyone.
Where possible:
- Give users only the permissions they require.
- Use
sudofor admin operations. - Avoid running applications as
root. - Remove inactive accounts.
- Review users and groups regularly.
- Protect sensitive configuration and credential files.
You can review local users with:
cut -d: -f1 /etc/passwdAnd check privileged accounts and groups according to your operating system's configuration.
The idea is simple, a compromised application or account should not automatically give unrestricted server control.
4. Keep the Server Patched
Hardening security is not a one-time configuration job. After a server is set up, software vulnerabilities are often found.
Installed packages and the operating system should be updated frequently.
Administrators often use
sudo apt update
sudo apt upgrade
Enable Automatic Security Updates
For supported Linux distributions, automatic security updates can help install important security patches without relying entirely on manual maintenance. Configure the appropriate package-management tools for your operating system, and verify which updates will be installed automatically. Test the configuration and monitor update results to reduce the risk of unexpected application changes.
Automatic updates are an operating-system configuration unless SharkCluster explicitly provides this capability through its control panel.
Updates should be scheduled and tested in accordance with the application's requirements in production environments.
Patching is not only for the operating system. Review:
- PHP versions
- Node.js runtimes
- Python packages
- Database servers
- Web servers
- Framework dependencies
- Application libraries
- Container images
A secure server may still be vulnerable even if it has an out-of-date application dependency.
Schedule updates on a regular basis and keep an eye out for security warnings about software running on your infrastructure.
5. Monitor Servers and Set Up Alerts
Preventive security controls reduce risk, but monitoring helps you find unexpected behavior.
Some useful signals to monitor include:
- CPU and memory usage
- Disk utilization
- Server availability
- Application errors
- Failed login attempts
- Service failures
- Unusual process activity
- SSL certificate expiration
- Database availability
Having centralized monitoring can help identify unusual activity easier than looking at individual servers.
For instance, when they occur concurrently with other unusual activity, repeated unsuccessful attempts at SSH authentication may call for further investigation.
Logs are also valuable when investigating an incident. Ensure that the appropriate application, system, web server, and authentication logs are accessible and protected from modification.
Actionable alerts should exist.Too many low-value notifications can lead to important security events being missed.
6. SSL/TLS Security Certificates
Use HTTPS in applications that handle personal information, APIs, login credentials, or other sensitive traffic.
SSL/TLS certificates enable browsers to verify the domain's certificate, in addition to encrypting client-server communication.
Make sure, after configuring HTTPS, that:
- The certificate matches the domain.
- The certificate hasn't expired.
- HTTP traffic is redirected to HTTPS where appropriate.
- TLS configuration follows current security recommendations.
- Renewal is automated or monitored.
Certificate expiration can cause avoidable downtime and browser security warnings. Monitoring certificate status should be part of regular infrastructure maintenance.
For applications managed through SharkCluster, SSL configuration and domain management can be incorporated into the broader server and application management workflow.
7. Review Services and Reduce the Attack Surface
Every service running on a server can potentially add on additional configuration requirements or vulnerabilities.
Periodically review listening ports and running services.
For example:
sudo ss -tulpnThis can help you locate services that are looking for network connections.
Rather than keeping a service available forever, disable or remove it if it's not needed.
The same is true for development tools and temporary services.On a production server, a useful debugging endpoint or test application should not remain publicly accessible.
With a smaller attack surface, infrastructure is typically easier to comprehend, monitor, and maintain.
8. SharkCluster's Built-In Security Approach
When infrastructure management and security operations are integrated as part of the same workflow, server hardening is easier.
SharkCluster makes it possible for infrastructure teams to manage operational tasks without treating each server as an independent system by providing a centralized environment for managing servers and applications.
Security-related operational tasks can include the following, depending on the configuration of the server and application:
- Managing server access and configuration
- Monitoring server health and metrics
- Reviewing alerts
- Managing application services
- Managing domains and SSL/TLS configuration
- Monitoring server and application status
- Performing infrastructure maintenance
This doesn't eliminate the need for secure configuration. Instead, it provides a centralized management layer that may help in organizing routine infrastructure operations.
The strongest security setup still depends on how administrators configure their servers, applications, credentials, networking, and access policies.
9. Create a Security Checklist That Can Be Reused
Create a security checklist for each production server instead of relying on memory.
A useful checklist might include:
Access
- SSH keys configured
- Password-based SSH authentication reviewed
- Inactive users removed
- Administrative privileges reviewed
- Private keys protected
Network
- Firewall enabled
- Required ports identified
- Unnecessary public ports blocked
- Database access restricted where appropriate
- Temporary services removed
Software
- Operating system patched
- Web server updated
- Runtime versions reviewed
- Application dependencies updated
- Database software maintained
Encryption
- HTTPS enabled
- SSL/TLS certificate valid
- Certificate renewal monitored
- HTTP-to-HTTPS behavior reviewed
Monitoring
- Server monitoring enabled
- Application monitoring enabled
- Authentication logs reviewed
- Service failures generate alerts
- Disk and resource utilization monitored
When managing multiple servers, security checklists are especially helpful because they provide a consistent baseline rather than manual inspection.
Security hardening is a process that continues.
A server cannot be completely secured by a single command. Effective server security hardening requires monitoring infrastructure, controlling access, encrypting traffic, reducing unnecessary exposure, and updating software.
Start with the fundamentals, such as securing SSH access, configuring a firewall, minimizing privileges, patching software, safeguarding application services, enabling HTTPS, and monitoring critical operational and security events.
Then make these practices repeatable across every production server.
With SharkCluster, infrastructure teams can manage servers, applications, monitoring, domains, and operational tasks from a centralized platform while maintaining control over the underlying server configuration.
Ready to build a more secure server environment?
Bring server provisioning, application management, monitoring, and day-to-day infrastructure operations into a single centralized platform with SharkCluster to begin managing your infrastructure.
Run this on your own VPS
Deploy servers and applications on infrastructure you own, managed from one panel — backups, caching, firewall and monitoring included.